Baku 18° C
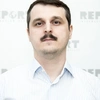
Nadir Novruzov: All possible risks must be taken into account when transitioning to CI/CD
- 02 October, 2026
- 17:03
Stay up to date with the top news!
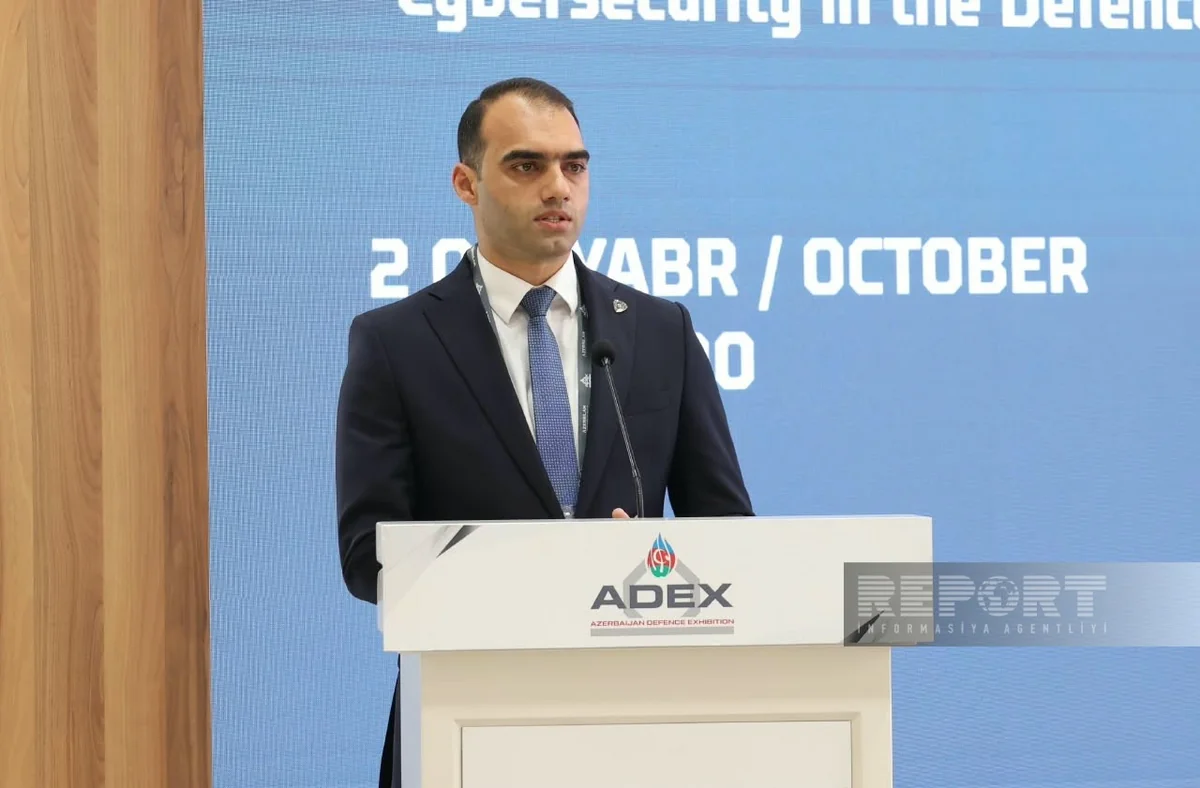
New security risks may arise as Azerbaijani government agencies and companies move from the FTP (File Transfer Protocol) used for transferring files to a more modern CI/CD environment, Nadir Novruzov, department head at the State Service of Special Communication and Information Security, said during a panel discussion held as part of ADEX 2026 – the 6th Azerbaijan International Defense Exhibition.
According to Report, Novruzov noted that while a transition to a CI/CD environment would accelerate software development and updates, it could also create new cybersecurity risks.
"Along with the security opportunities it brings, the transition to a CI/CD environment will also create certain security problems. We see this, and it will require a comprehensive approach. We cannot simply make the transition and allow everything," he said.
Speaking about audits of state information resource systems, Novruzov also outlined the main problems that can prolong the inspection process.
He said one of the first difficulties encountered during audits was related to technical problems arising at the deployment stage.
"In practice, we face certain difficulties. First, during deployment by the company or agency that developed the system, there may be difficulties with configuration or something may not work properly. We want to inspect the system, but either the system itself or some part of it does not work. In that case, our inspection remains incomplete," Novruzov said.
He noted that once the technical problems are resolved, the audit has to be conducted again, extending the overall process.
"In such cases, we have to apply again. After they resolve the problems, we carry out another inspection," he said.
Novruzov added that delays in fixing security vulnerabilities identified during audits were another major factor prolonging the process.
"One of the issues that prolongs the process the most is that the system is checked, vulnerabilities are identified and a request is made to eliminate them. The remediation period is prolonged, or when we recheck vulnerabilities that are said to have been fixed, we see that vulnerabilities still remain. This inevitably extends the process," he said.
Author